For MSPs

Run every client's handover on your brand, and prove it.

Per-client branding and domains, a PSA-linked workflow, and audit evidence your clients and their cyber-insurers can actually read. On a tool whose vendor can't read the secret.

Trial coming soon Talk to us
One console

Every client, cleanly separated.

  • Each client sits under your org with its own branding, custom domain, contacts and directory.
  • The handover page is branded as them, on their domain, never a generic vendor page.
  • Client separation is enforced in the data model, not just the UI, so one client can never see another's records.
app.safehanded.com/app/branding
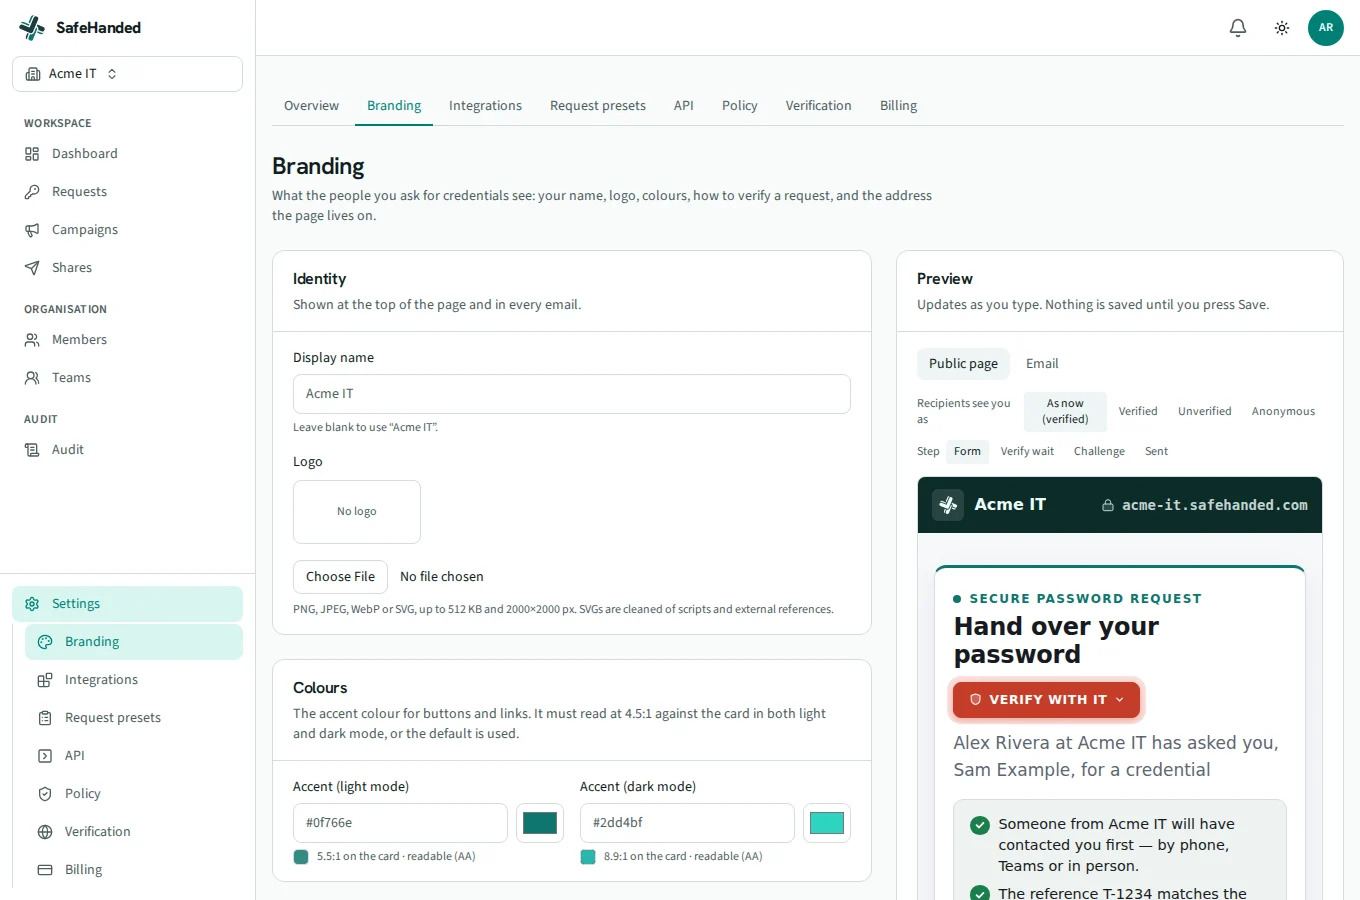
The branding editor: per-client logo, colours, contacts and a live preview of that client's handover page.
Per-client branding, with a live preview of the real page.
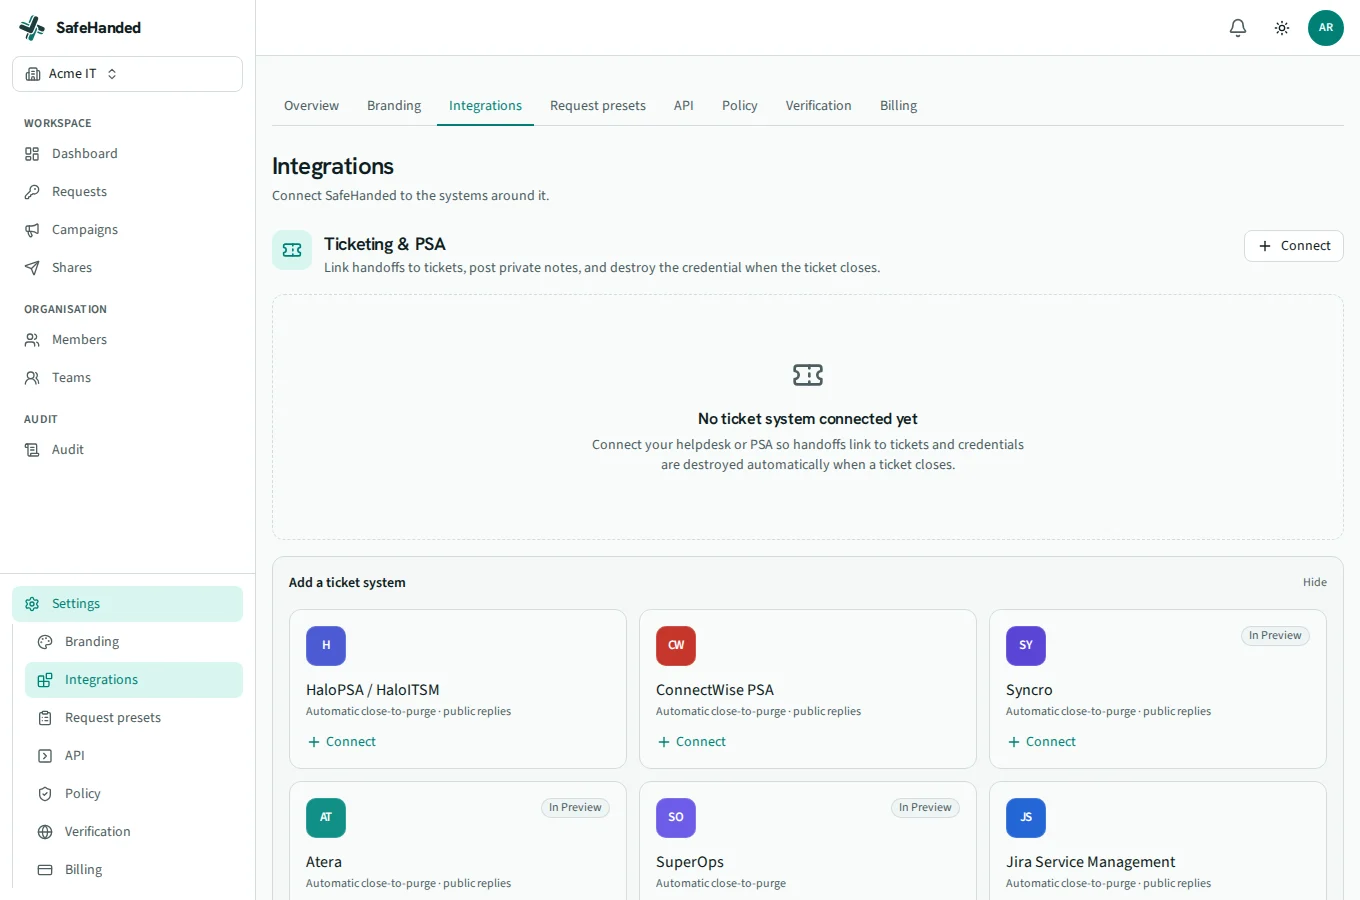
app.safehanded.com/app/integrations
The integrations page: ticketing, directory, chat and SIEM connectors.
Integrations, ticketing, directory, chat and SIEM.
In the ticket

It starts and ends in the PSA.

  • Create a request from ServiceNow, Jira Service Management, Freshservice and four other fully supported helpdesks. In preview: HaloPSA, ConnectWise PSA, Syncro, Atera, SuperOps, HubSpot and a generic webhook. Or use the API.
  • A private note is written back to the ticket at each step, so the record stays with the work.
  • The credential purges itself when the ticket closes, nothing orphaned across dozens of clients.
Evidence

Answer the questionnaire with proof.

Cyber-insurance renewals and client audits ask the same question: how do you handle user credentials? Instead of a paragraph of assurances, hand them evidence.

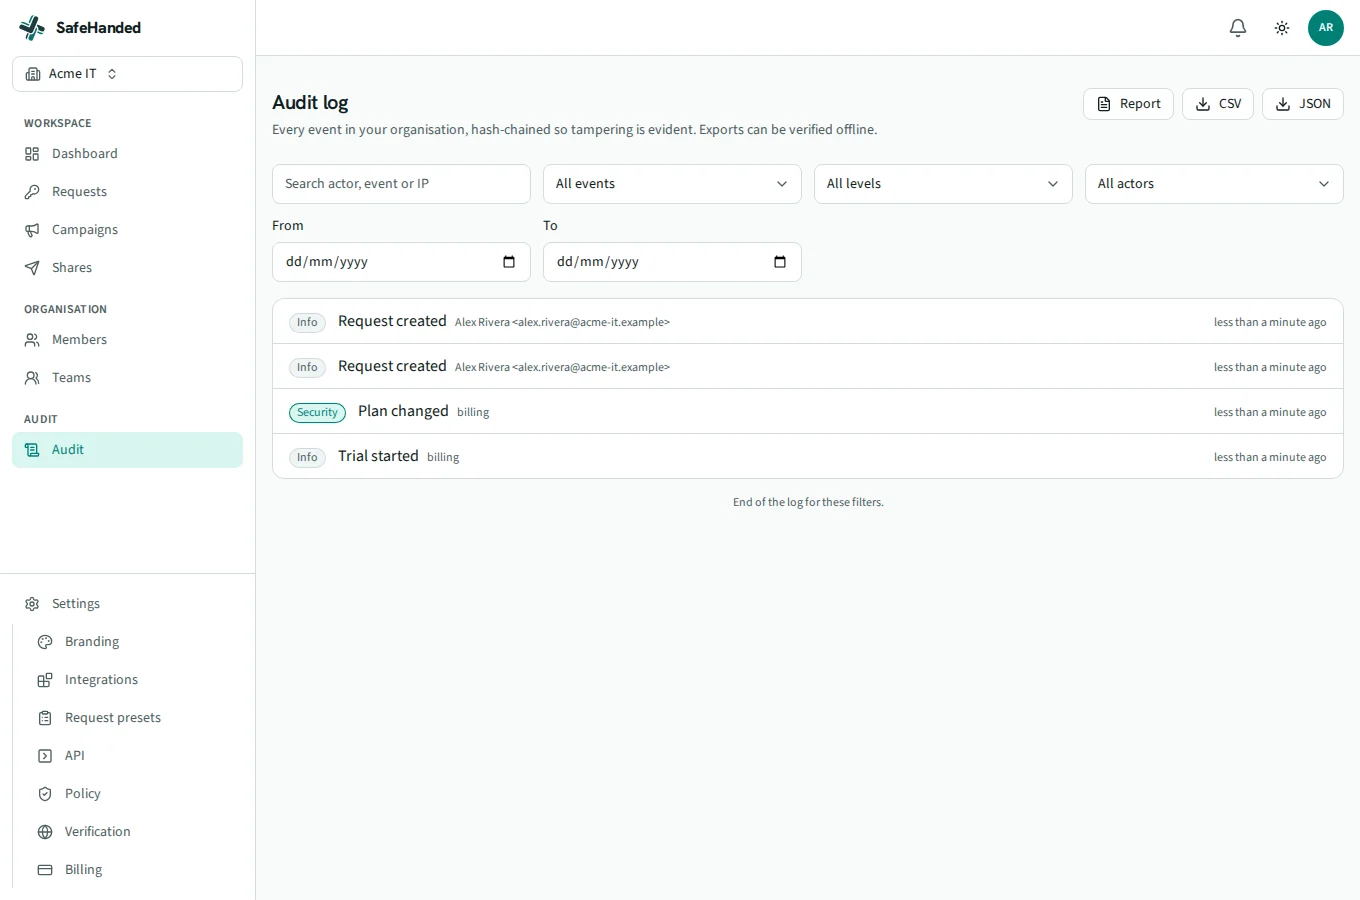
  • A log per client of who asked for, opened and destroyed every password. It can't be quietly edited.
  • A signed certificate for any handover, to hand to the client or their auditor.
  • Export the log, or send it to the client's security monitoring tool.
Read the security model →
app.safehanded.com/app/audit
The audit log: every event with who did it, when, from where and the outcome, ready to export.
A log per client, ready to export.
Why it matters

The vendor can't read your clients' secrets.

Most link tools can decrypt every secret they hold, so a breach at the vendor, or a rogue operator, is a breach of every client you serve. SafeHanded only ever stores ciphertext, sealed to one technician's passkey. There is no readable secret on our side to leak, subpoena or misconfigure.

SEPARATION

Per-client isolation

Branding, domains, directories and audit trails are scoped to the client, enforced below the UI.

RECOVERY

Leavers handled

Portable keys, an optional org recovery key and tested offboarding, so a technician leaving never strands a client's credential.

SCALE

Wire it in

Bulk campaigns, a public API (OpenAPI 3.1) and signed webhooks to fit SafeHanded into your existing automation.

Pricing

Priced for a practice.

One flat plan for your whole client base, with technicians so cheap that seats never block adoption. Auditors, including your clients' auditors, are always free.

MSP plan
£149/month

£1,490/year · 10 technicians included, then £8 each

Trial coming soon Compare plans
  • Unlimited clients with per-client branding and custom domains.
  • Every ticketing adapter: seven fully supported helpdesks, plus six more and the generic webhook in preview.
  • The public API and SIEM streaming, plus two years of audit retention.
  • A 14-day trial with no card, and Auditors free on every plan.
Get started

Give every client a safe way to be handed a password.

Start a 14-day MSP trial with no card, bring in a client or two, wire up your PSA, and see the evidence for yourself before you commit.

Trial coming soonTalk to us